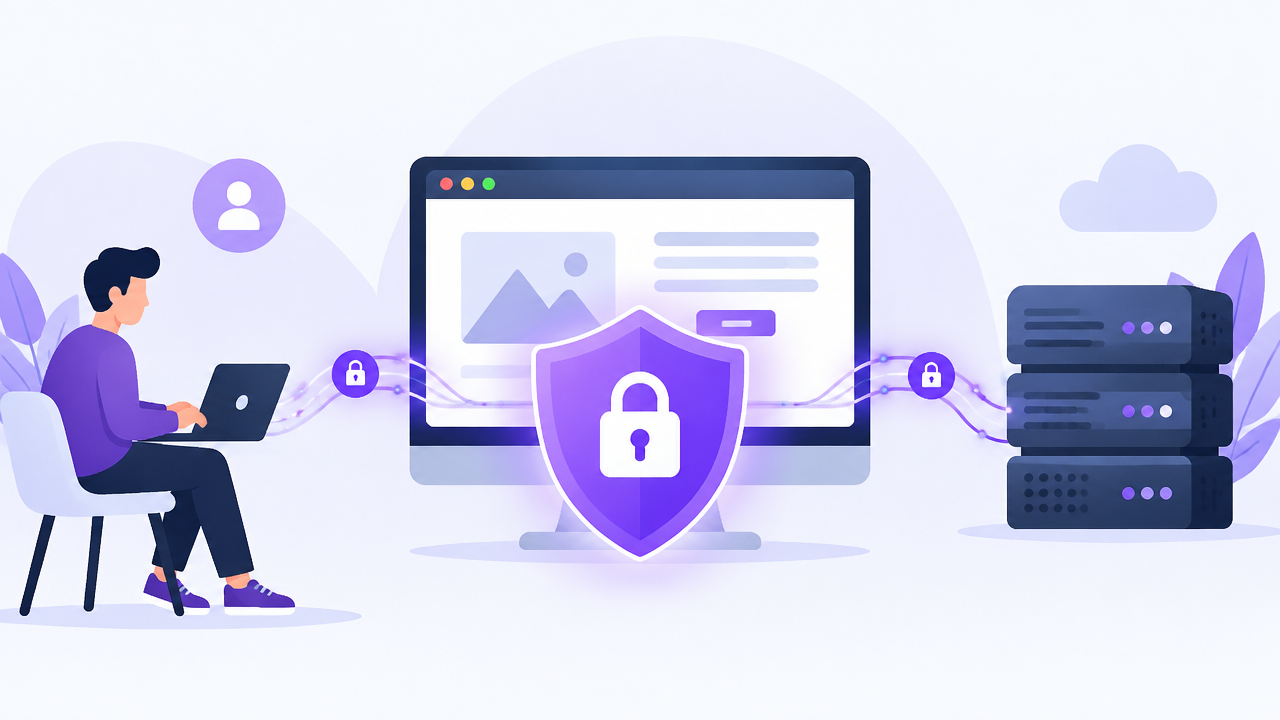
An SSL certificate enables a website to use HTTPS, helping browsers verify the server and establish an encrypted connection. I recommend one for every public website, not only online stores, because login details, contact forms, and ordinary browsing can all involve data worth protecting. Correct installation and ongoing checks matter as much as getting the certificate.
Key points about website certificates
A certificate helps authenticate a website and supports encryption through TLS.
SSL is the legacy name; modern HTTPS connections use TLS.
DV, OV, and EV describe identity checks, while wildcard and multi-domain describe coverage.
A certificate does not guarantee that a website is trustworthy or malware-free.
Expiry, hostname mismatch, incomplete chains, and mixed content can undermine HTTPS.
What does an SSL certificate do?
A certificate helps a browser confirm that it is connecting to a server authorized for the requested domain. During a TLS handshake, the server presents its certificate and proves control of the associated private key. The browser checks the certificate’s validity and trust chain, then the connection can establish encryption for data exchanged during the session. The TLS 1.3 protocol specification describes certificate-based authentication in this handshake.
This protects data in transit from being easily read or altered by someone observing the connection. It is useful for checkout pages and account logins, but also for basic contact forms, admin pages, and everyday visits. A certificate is one part of website security, not a substitute for secure application code, access controls, or safe data handling.
SSL, TLS, and HTTPS describe different things
HTTPS is HTTP carried over a secure TLS connection. SSL is the older protocol name that remains common in phrases such as “SSL certificate,” but modern web connections use TLS. In practical terms, site owners usually buy or install a certificate, configure their server for TLS, then serve pages over HTTPS.
After enabling HTTPS, check that every important hostname is covered and that HTTP URLs redirect to the corresponding HTTPS pages. Also inspect embedded resources: an HTTPS page that loads scripts, stylesheets, or other assets over HTTP may have mixed-content problems. I recommend checking the site’s supported TLS versions and reviewing its mixed-content configuration as part of the setup.
Certificate types differ by validation and coverage
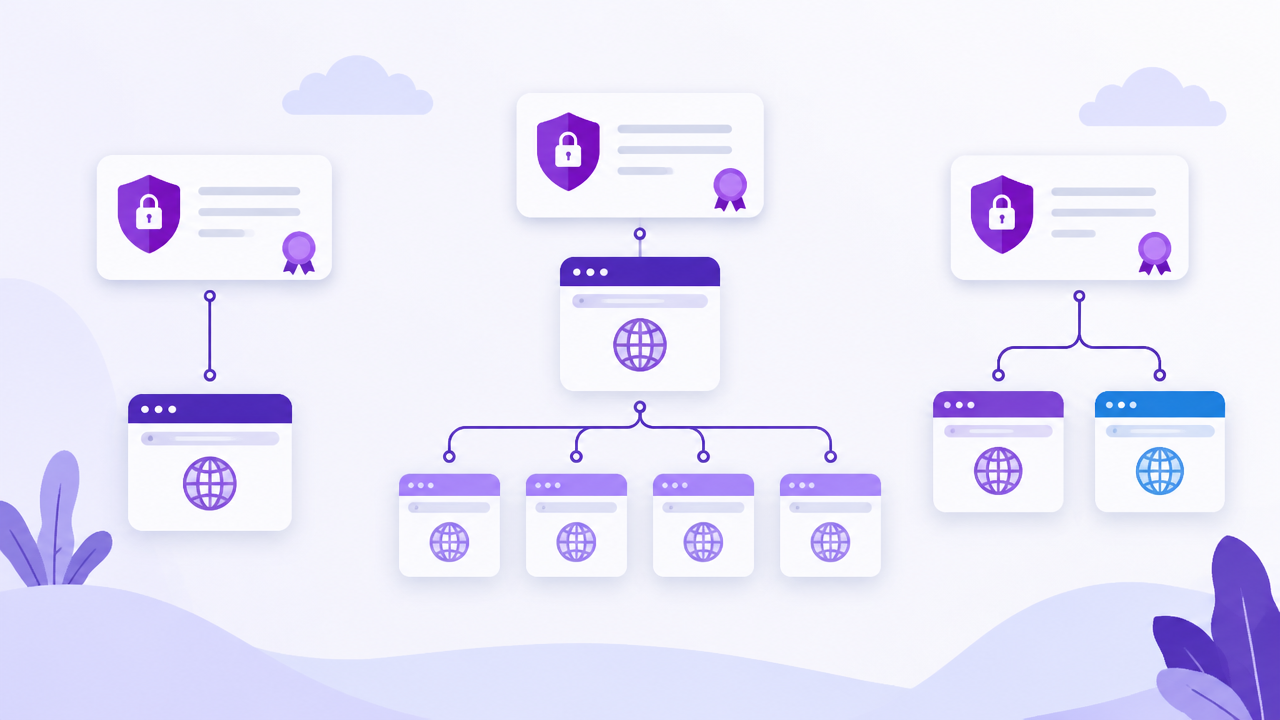
Choose a certificate based on what identity needs verification and which hostnames need protection. The three familiar validation levels are DV, OV, and EV. They describe the checks performed by the issuing authority, not separate grades of encryption.
Type | What it generally validates | Typical use |
|---|---|---|
DV | Control of the domain | Personal sites, blogs, and many business websites |
OV | Domain control and organization details | Organizations that want business identity checked |
EV | More extensive checks of the legal organization | Organizations that need the additional vetting process |
Coverage is a separate choice. A single-domain certificate covers a specified hostname; a wildcard can cover eligible subdomains, and a multi-domain certificate can cover several listed hostnames. Check the certificate’s names against every live version of the site, including the root domain and any subdomains you use. 37 Audits’ certificate auditor can help review certificate details.
A certificate is not a guarantee that a site is safe
HTTPS protects the connection, but it does not certify the website’s business practices or the safety of everything it serves. A phishing page can use HTTPS, and a legitimate site can still have vulnerable software or compromised accounts. I treat the padlock as a signal about the connection, not a blanket endorsement of the site.
That distinction matters for site owners, too. Certificates should be part of a wider security routine that includes updates, strong authentication, secure headers, and careful handling of user information. For visitor trust, a valid certificate is a baseline expectation. If a browser shows a warning, users may leave before deciding whether they trust the business.
HTTPS supports search consistency, but it cannot fix SEO by itself
HTTPS is useful for both visitors and search hygiene, but it does not replace crawlability, useful content, or correct indexing signals. Google says it generally prefers HTTPS URLs as canonical versions of equivalent pages, while noting that certificate problems, insecure dependencies, and redirects back to HTTP can interfere with that preference. Its HTTPS canonicalization guidance is especially useful when migrating an established site.
After switching, update internal links, canonical tags, sitemaps, and redirects so they consistently point to HTTPS. Check both www and non-www hostnames if your site supports them. A valid certificate on one hostname does not automatically cover another, and a partial migration can leave duplicate URLs or warning pages behind.
How should I maintain a certificate?
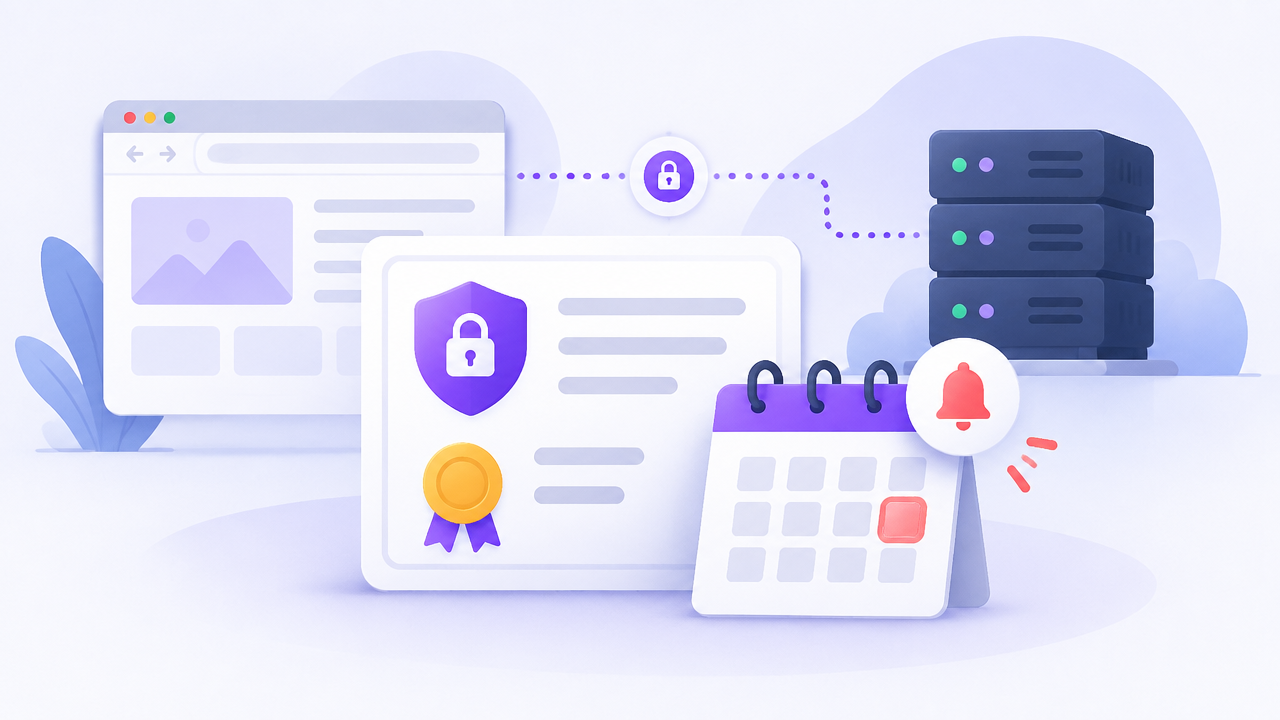
Certificate management is an ongoing task because certificates expire and site configurations change. I recommend documenting the covered hostnames, renewal method, responsible owner, and alert destination. Automated renewal helps, but it still needs monitoring: a failed challenge, DNS change, or deployment issue can prevent renewal or leave the new certificate unapplied.
Check expiration dates and set alerts well before renewal is due.
Confirm the certificate matches every public hostname.
Verify that the complete trust chain is served correctly.
Test redirects and scan for insecure resources after deployment.
Recheck TLS settings after hosting or infrastructure changes.
37 Audits provides continuous website checks and alerts, including certificate and related technical audits. I would use ongoing monitoring alongside a deployment checklist so that a certificate issue is caught before visitors encounter a warning. For more context on why missed renewal can disrupt a site, see this guide to certificate expiration risks.
Frequently asked questions
What does an SSL certificate do?
An SSL certificate identifies a website to browsers and enables an encrypted connection using TLS. It helps protect information while it travels between a visitor and the site, but it does not prove that the business is honest or that the website is free from malware.
Is SSL still used, or is it called TLS?
SSL is the older protocol name; modern secure web connections use TLS. People still commonly say “SSL certificate,” but the certificate is used during a TLS handshake to help authenticate the server and establish keys for an encrypted connection.
What are the three main certificate validation types?
The three common certificate validation levels are Domain Validation (DV), Organization Validation (OV), and Extended Validation (EV). They differ in how much identity information the issuer checks, not in the strength of the encryption a correctly configured TLS connection can use.
Does HTTPS improve Google rankings?
HTTPS can support search visibility, but it is not a shortcut to higher rankings. Google prefers HTTPS versions of equivalent URLs in many cases, yet a bad certificate, insecure dependencies, or redirects to HTTP can interfere with that preference. Useful content and sound technical SEO still matter.
What can trigger an HTTPS certificate warning?
A browser warning can appear when a certificate has expired, does not match the hostname, or cannot be traced to a trusted certificate authority. Insecure page resources can also create warnings or browser security issues, even when the main page loads over HTTPS.